

Healthcare Braces for Machine-Speed Cyberattacks as AI Compresses Threat Timelines to Milliseconds
Coalition for Health AI assembles nearly 100 experts to build defensive playbooks against frontier AI threats that can execute attacks faster than human response times.
The healthcare sector is confronting a fundamental shift in cybersecurity dynamics as frontier artificial intelligence models collapse attack timelines from days or weeks into seconds or milliseconds—a compression that may soon require semi-autonomous defensive systems to counter threats moving at machine speed. In response, the Coalition for Health AI (CHAI) has launched a dedicated cybersecurity task force to develop practical defensive frameworks tailored to healthcare's unique vulnerabilities.
Nearly 100 Experts Mobilized for December Delivery
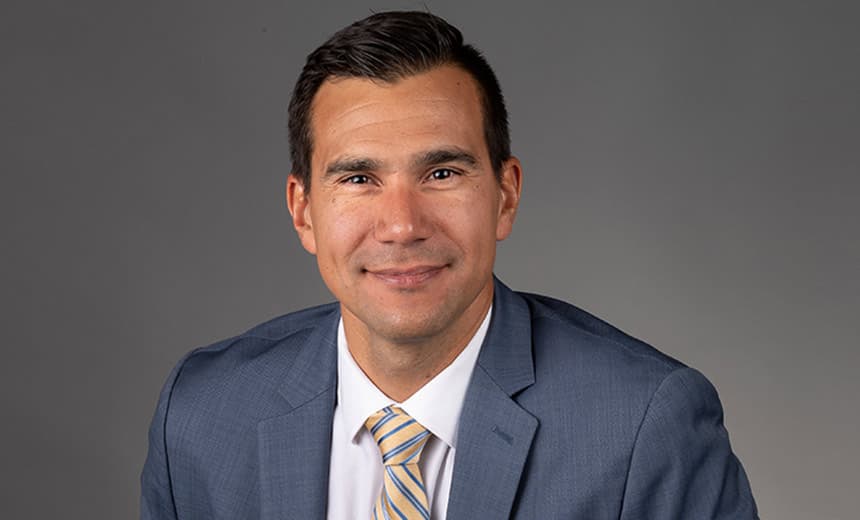
CHAI's new cybersecurity workgroup brings together nearly 100 members, including chief information security officers and security specialists from health systems, payers, and the Health Information Sharing and Analysis Center (H-ISAC). Led by CHAI CEO Dr. Brian Anderson—a physician who previously served as chief digital health physician at MITRE and worked with the White House COVID Task Force—the group is targeting December 2024 for the first public release of its defensive playbooks.
The task force will convene bi-weekly work sessions to collaboratively develop three core deliverables: a defensive playbook, an offensive playbook, and a frontier AI cyber risk assessment tool. These materials are designed to provide actionable technical guidance for protecting protected health information, maintaining clinical operations during attacks, and implementing defensive measures against AI-accelerated threats including PHI leakage, ransomware, and clinical downtime.
Targeting Rural and Under-Resourced Providers
The playbooks are being developed with particular attention to rural and safety net providers, who often lack dedicated cybersecurity teams yet face the same sophisticated threats as large health systems. By providing reference implementations and practical guidance, CHAI aims to democratize access to advanced defensive strategies across the healthcare ecosystem.
Some highly technical materials may require vetting before public release, according to the initiative's framework, reflecting the sensitive nature of certain cybersecurity countermeasures that could be exploited if widely disseminated without controls.
Implications for Health Tech and AI Governance
For health technology companies and AI developers, CHAI's cybersecurity frameworks are likely to establish de facto security standards for agentic AI tools that access external data or endpoints. These guidelines may influence regulatory expectations and become criteria in vendor selection processes as healthcare organizations seek to implement AI systems that meet emerging security benchmarks.
The initiative represents CHAI's strategic expansion beyond clinical AI validation into operational security domains, positioning the organization as a comprehensive AI governance authority in healthcare. This evolution signals the maturation of health AI oversight to address not only the accuracy and safety of clinical algorithms but also the security infrastructure required to deploy AI systems in an increasingly hostile threat environment where attackers wield the same advanced technologies as defenders.
Sources
Reporting & accountability
How we maintain accuracy
Health AI Central separates reported facts, analysis, and public-source data. Readers can review our standards, request a correction, or consult the relevant research methodology before relying on a claim.